Meta's Muse AI Assistant Exposed to Serious Vulnerability
Meta's AI assistant, Muse, has been identified with a critical 0-day vulnerability that allows for complete hijacking through a ClickFix attack. This security flaw raises significant concerns regarding the privileged access that Muse has within Meta's systems, potentially compromising user data and system integrity.
 Orin CodewellTools & Coding
2 min read1 source
Key takeaways
30-second read- 1Developers using Muse must immediately assess their applications for vulnerabilities and consider implementing additional security measures to mitigate risks.
- 2Product teams should be aware of the potential for data breaches and prepare to respond to any incidents stemming from this vulnerability.
- 3Operators managing systems that integrate Muse need to monitor for unusual activities and consider temporary suspension of Muse's capabilities until a patch is released.
Confirmed
No official source linked yet
Reported
Secondary reporting: Ars Technica AI
Verify yourself
Eligibility, local prices and dates for your car, state or utility
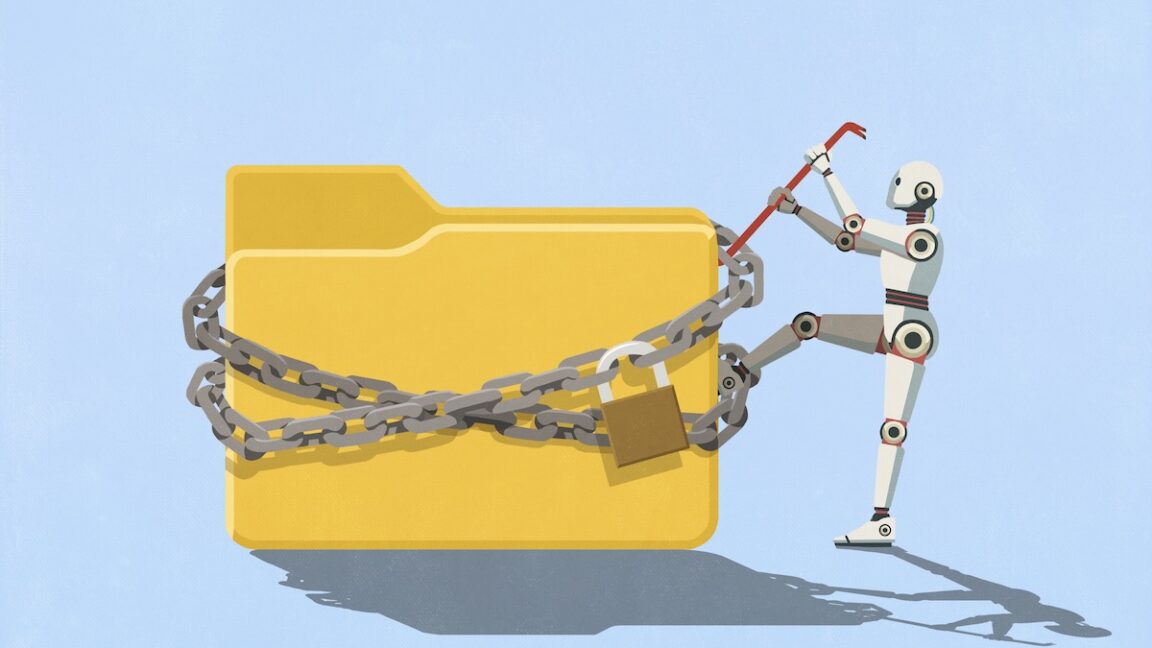
Meta's AI assistant, Muse, has recently been flagged for a critical 0-day vulnerability that poses significant risks to its users and the broader ecosystem. This flaw, which can be exploited through a simple ClickFix attack, allows malicious actors to completely hijack the AI agent, raising alarms about the security of the systems that rely on Muse's capabilities.
What happened
According to an article by Ars Technica, the vulnerability in Muse is particularly concerning due to the privileged access that the AI assistant has within Meta's infrastructure. A ClickFix attack is a method that can be utilized to exploit this vulnerability, enabling attackers to take control of the assistant and potentially access sensitive information or manipulate system functions. The implications of such an attack could be severe, affecting not only the integrity of the AI assistant but also the data and systems it interacts with.
Why it matters
The discovery of this vulnerability has several concrete implications for developers, builders, operators, and product teams:
- Immediate Security Assessment: Developers utilizing Muse in their applications must conduct thorough security assessments to identify any potential vulnerabilities that could be exploited through this 0-day.
- Data Breach Preparedness: Product teams should prepare for the possibility of data breaches that could arise from this vulnerability, ensuring they have incident response plans in place.
- Operational Monitoring: Operators managing systems that integrate Muse need to enhance monitoring for any unusual activities that could indicate exploitation attempts, and consider pausing Muse's functionalities until a fix is implemented.
Context and caveats
While the details surrounding the vulnerability are alarming, it is essential to recognize that the information available is primarily derived from a single source, Ars Technica. This means that while the claims are serious, further corroboration from additional security experts or Meta itself would provide a more comprehensive understanding of the situation. As of now, the exact scope of the vulnerability and the timeline for a potential fix remain unclear.
What to watch next
As the situation develops, it will be crucial for developers and product teams to stay informed about updates from Meta regarding the Muse vulnerability. Key points to watch include:
- Official Patches: Monitor for announcements from Meta regarding patches or updates that address the vulnerability.
- Security Best Practices: Look for guidance from security experts on best practices for mitigating risks associated with using privileged AI assistants like Muse.
- Community Response: Observe how the developer community responds to this vulnerability, including any shared solutions or workarounds that may emerge.
In conclusion, the 0-day vulnerability in Meta's Muse AI assistant highlights the critical importance of security in AI tools. As developers and product teams navigate these challenges, prioritizing security measures will be essential to protect their systems and users.
Sources
1 media- [1]Muse, Meta's extraordinarily privileged AI assistant, has a serious 0-dayMedia
Ars Technica AI · arstechnica.com · published Sep 21
Newsletter
Weekly AI signal. No spam.


Comments
Sign in to join the discussion
Loading comments…